> For the complete documentation index, see [llms.txt](https://docs.apono.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.apono.io/docs/additional-integrations/network-management/zscaler-private-access.md).

# Zscaler Private Access

Create an integration to manage access to a ZPA instance

Zscaler Private Access (ZPA) is a cloud-native service that provides secure, zero-trust access to private applications running in the public cloud or a data center.

Through this integration, Apono discovers Zscaler ZPA access policy rules and uses them to manage access. When Apono grants access, it creates a temporary access policy rule by copying the scope of the selected rule and modifying the user assignment for the requester. The requester receives access to all application segments allowed by the selected rule.

***

### Limitations

Before you integrate Zscaler ZPA, review the following limitations:

* Zscaler limits each ZPA tenant to **2,000 access policy rules**. Apono creates one temporary access policy rule for each active grant, and these rules count toward that limit. If your tenant is close to the limit, contact Zscaler Support.
* The ZPA API allows **20** `GET` requests and **10** `POST`, `PUT`, or `DELETE` requests per **10-second interval from a single IP address**. Apono queues requests and honors the `Retry-After` header, so grants and revokes may take longer to complete when many operations run through the same connector at the same time.
* Apono reports a grant as successful after the access policy rule is created. However, Apono **cannot** verify that the end user can reach the application. Access may still be denied by a higher-priority block rule, ZPA context criteria such as location or device posture, or an unavailable Zscaler Client Connector.
* Apono discovers only enabled **ALLOW** access policy rules. Disabled rules and block rules are not discovered and cannot be used in access flows.
* The integration **only supports the ZPA Legacy API**. Tenants that use OneAPI with Authentication Service (formerly ZIdentity) are not supported.
* Microtenants are not supported. Apono discovers and manages access policy rules in the default tenant only.
* Each integration supports a single identity provider (IdP). To manage access policy rules for multiple IdPs, create a separate integration for each IdP.

***

### Prerequisites

<table><thead><tr><th width="260">Item</th><th>Description</th></tr></thead><tbody><tr><td><strong>Apono Connector</strong></td><td><p>On-prem connection serving as a bridge between a Zscaler instance and Apono:</p><ul><li><a href="/docs/aws-environment/apono-connector-for-aws.md">AWS</a></li><li><a href="/docs/azure-environment/apono-connector-for-azure.md">Azure</a></li><li><a href="/docs/gcp-environment/apono-connector-for-gcp.md">GCP</a></li><li><a href="/docs/kubernetes-environment/apono-connector-for-kubernetes.md">Kubernetes</a></li></ul></td></tr><tr><td><strong>Zscaler ZPA Account Access</strong></td><td>Zscaler ZPA account with permission to create admin roles and API keys</td></tr><tr><td><strong>Zscaler Customer ID</strong></td><td><p>Unique Zscaler identifier used to scope API requests to your tenant</p><p><br>Follow these steps to obtain the customer ID from the ZPA Admin Portal:</p><ol><li>From the navigation, click <strong>Configuration &#x26; Control > Public API > API Keys</strong>. The <strong>API Keys</strong> page appears.</li><li>Click the <strong>Menu</strong> icon.</li><li>Copy the <strong>Customer ID</strong>.</li></ol></td></tr></tbody></table>

***

### Obtain integration values

Apono identifies the requester for the access policy rule by email address. The requester's email address in Apono must match the email stored in the configured ZPA IdP. Apono does not map between different user identities. To configure this matching behavior, identify the IdP, determine whether its policy attributes use SCIM or SAML, and identify the exact attribute that contains the user's email address.

These values are configured in Apono as the **IdP**, **Policy Attribute Protocol**, and **Policy Email Attribute**.

#### Determine the Policy Attribute Protocol

Follow these steps in the ZPA Admin Portal:

1. From the side navigation, click **Authentication > User Authentication > IdP Configuration**. The **IdP Configuration** page appears.
2. From the **Name** column, identify the IdP that provisions your users and copy its display name. Use this value for the **IdP** setting in the Apono integration config.
3. Open the IdP configuration for editing. Use the following table to determine the **Policy Attribute Protocol** value for the Apono integration.

<table><thead><tr><th width="337.71099853515625">IdP Configuration</th><th>Policy Attribute Protocol</th></tr></thead><tbody><tr><td><p><strong>SAML Attributes for Policy: Enabled</strong></p><p>and</p><p><strong>SCIM Attributes for Policy: Disabled</strong></p></td><td>SAML</td></tr><tr><td><p><strong>SAML Attributes for Policy: Disabled</strong></p><p>and</p><p><strong>SCIM Attributes for Policy: Enabled</strong></p></td><td>SCIM</td></tr></tbody></table>

#### Obtain the Policy Email Attribute

![SAML Attributes and SCIM Attributes pages](https://1094436629-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fv6MBfUGvblSdAz31yJXm%2Fuploads%2Fgit-blob-7f31ddae40ca93b354ac9bd9ed7905ff124f4ab8%2Funknown%20\(7\).png?alt=media)

For the Apono integration, the **Policy Attribute Protocol** and **Policy Email Attribute** values must correspond to the same IdP and attribute type. If the protocol is SCIM, use the email attribute from that IdP's **SCIM Attributes** list. If the protocol is SAML, use the email attribute from that IdP's **SAML Attributes** list.

{% hint style="danger" %}
A mismatched protocol or attribute can prevent the access policy rule from matching the requester, causing the grant to fail without an error.
{% endhint %}

Follow these steps to obtain the policy email attribute:

1. Open the attribute list. Expand **SCIM** or **SAML** below for instructions.

<details>

<summary><strong>SCIM</strong></summary>

1. From the side navigation, click **Authentication > User Authentication > SCIM Attributes**. The **SCIM Attributes** page appears.
2. From the dropdown menu, select the same IdP that was opened to determine the policy attribute protocol. The IdP attributes appear.

</details>

<details>

<summary><strong>SAML</strong></summary>

1. From the side navigation, click **Authentication > User Authentication > SAML Attributes**. The **SAML Attributes** page appears.
2. Filter the list by the name of the same IdP that was opened to determine the policy attribute protocol.

</details>

2. Copy the value from the **SCIM Attribute** or **SAML Attribute** column that contains the user email address, for example **emails.value** (SCIM) or **email-saml-test** (SAML).

{% hint style="warning" %}
Do **not** copy the display name shown in the ZPA Admin Portal.
{% endhint %}

***

### Create Zscaler ZPA credentials for the Apono connector

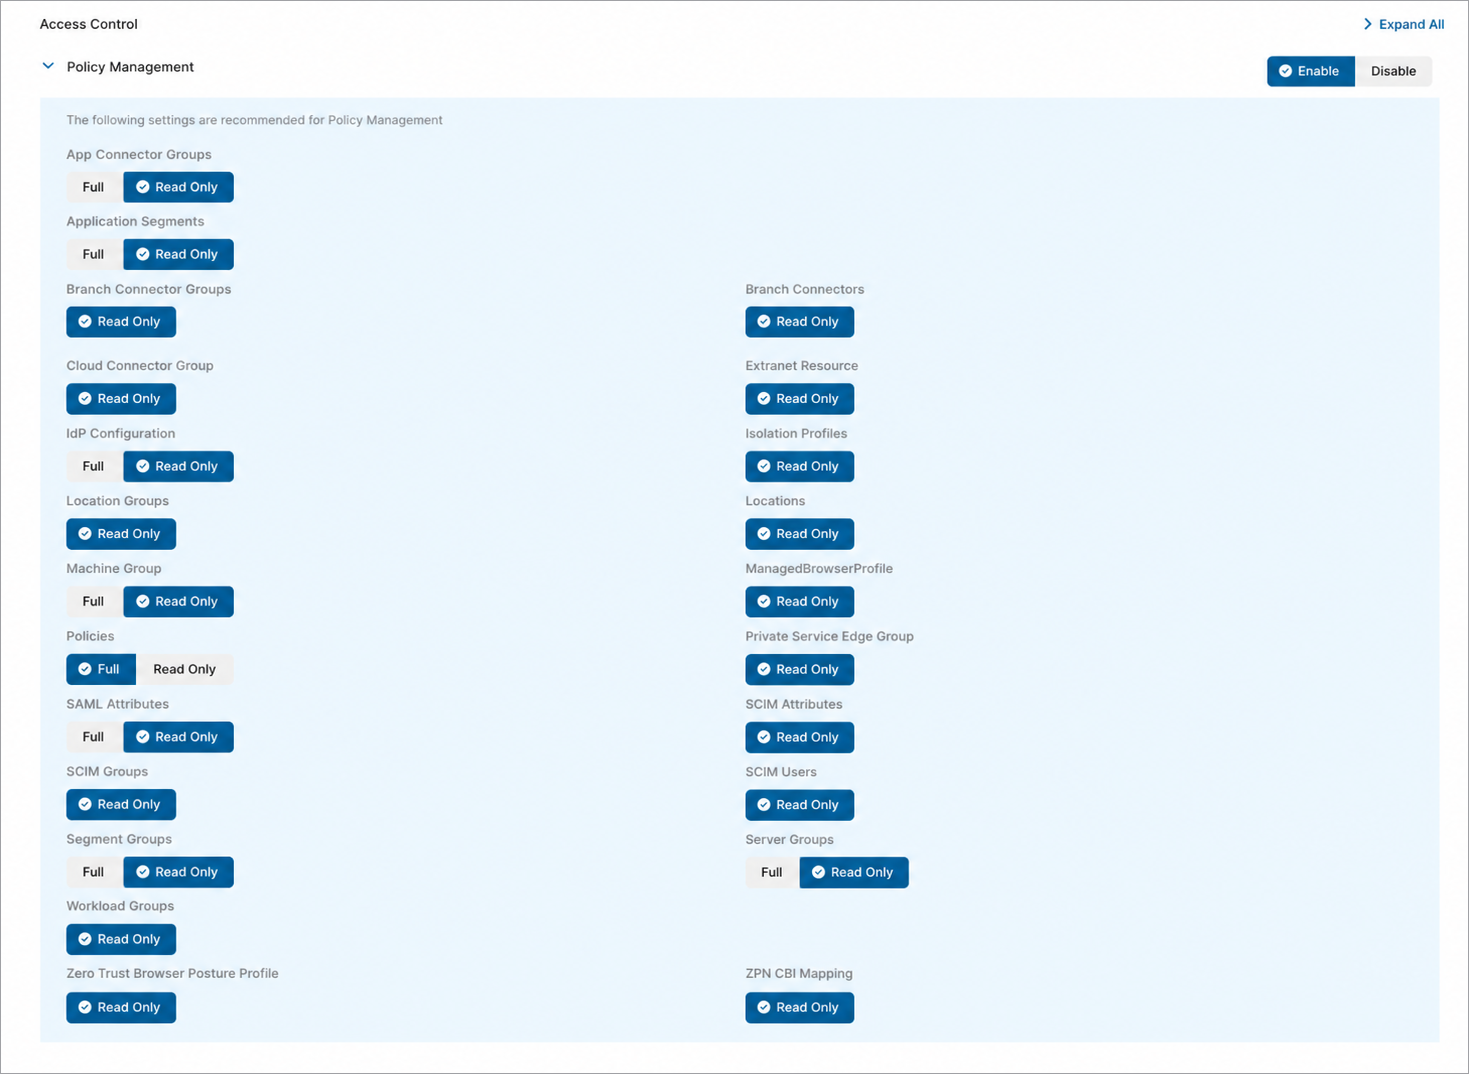
You must create API credentials in your ZPA Admin Portal for the Apono connector. The API key must be assigned a role that can manage access policy rules and read the IdP attribute configuration.

<figure><img src="https://1094436629-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fv6MBfUGvblSdAz31yJXm%2Fuploads%2Fgit-blob-225c111a8f9afe9fdea6748863a99b39d0c54a47%2Fzscaler-policy-management-access-control.png?alt=media" alt=""><figcaption><p>Policy Management Access Control in Zscaler ZPA</p></figcaption></figure>

Follow these steps to obtain the credentials:

1. From the side navigation, click **Configuration & Control > Administration Control > Roles** tab.
2. Click **+ Add**. The **Add Role** page appears.
3. Enter a descriptive **Name** for the role, such as *Apono Connector*.
4. (Optional) Enter a **Description** for the role.
5. Under **Access Control**, click **Enable** for **Policy Management**. The section expands.

{% hint style="info" %}
Leave all other **Access Control** scopes disabled.
{% endhint %}

6. Verify the following **Policy Management** permissions are set.

{% hint style="info" %}
These are the default settings. Other permissions can be adjusted to align with your organization's policies.
{% endhint %}

<table><thead><tr><th width="216.868896484375">Permission</th><th>Value</th></tr></thead><tbody><tr><td><strong>IdP Configuration</strong></td><td><strong>Read Only</strong></td></tr><tr><td><strong>Policies</strong></td><td><strong>Full</strong></td></tr><tr><td><strong>SAML Attributes</strong></td><td><strong>Read Only</strong></td></tr><tr><td><strong>SCIM Attributes</strong></td><td><strong>Read Only</strong></td></tr></tbody></table>

7. Click **Save**.
8. Click **Configuration & Control > Public API > API Keys**. The **API Keys** page appears.
9. Click **+ Add**.
10. Select the role created in steps **1-7**.
11. Click **Save**. The **Client Secret** pop-up window appears.
12. Copy and save the **Client Secret**.

{% hint style="warning" %}
Zscaler only displays the client secret once.
{% endhint %}

13. Close the pop-up window.
14. Copy the **Client ID**.
15. Using the client secret (step **12**) and client ID (step **14**), create a secret for the Apono connector. Use the following key-value pair structure when generating the secret. Be sure to replace `<ZPA_CLIENT_ID>` and `<ZPA_CLIENT_SECRET>` with the actual values.

{% code overflow="wrap" expandable="true" %}

```json
"client_id": "<ZPA_CLIENT_ID>",
"client_secret": "<ZPA_CLIENT_SECRET>"
```

{% endcode %}

{% hint style="success" icon="lightbulb" %}
You can also input the API credentials directly into the Apono UI during the [integration process](/docs/connectors-and-secrets/apono-integration-secret.md#apono).
{% endhint %}

***

### Integrate Zscaler ZPA

{% hint style="success" %}
You can also use the steps below to integrate with Apono using Terraform.

In step **12**, instead of clicking **Confirm**, follow the **Are you integrating with Apono using Terraform?** guidance.
{% endhint %}

Follow these steps to complete the integration:

1. On the [**Catalog**](https://app.apono.io/catalog?search=mongodb+atlas) tab, click **Zscaler ZPA**. The **Connect Integration** page appears.
2. Under **Discovery**, select one or multiple resource types.

{% hint style="info" %}
Apono automatically discovers and syncs all the instances in the environment. After syncing, you can manage access flows to these resources.
{% endhint %}

3. Click **Next**. The **Apono connector** section expands.
4. From the dropdown menu, select a connector. Choosing a connector links Apono to all the services available on the account where the connector is located.

{% hint style="success" %}
If the desired connector is not listed, click **+ Add new connector** and follow the instructions for creating a connector ([AWS](/docs/aws-environment/apono-connector-for-aws.md), [Azure](/docs/azure-environment/apono-connector-for-azure.md), [GCP](/docs/gcp-environment/apono-connector-for-gcp.md), [Kubernetes](/docs/kubernetes-environment/apono-connector-for-kubernetes.md)).
{% endhint %}

5. Click **Next**. The **Integration Config** section expands.
6. Define the **Integration Config** settings.

   <table><thead><tr><th width="224">Setting</th><th>Description</th></tr></thead><tbody><tr><td><strong>Integration Name</strong></td><td>Unique, alphanumeric, user-friendly name used to identify this integration when constructing an access flow</td></tr><tr><td><strong>Customer ID</strong></td><td><strong>(Required)</strong> Unique Zscaler identifier used to scope API requests to your tenant</td></tr><tr><td><strong>Policy Attribute Protocol</strong></td><td><p><strong>(Required)</strong> Identity attribute protocol Apono uses when writing access policy rules<br></p><p><strong>Options</strong>:</p><ul><li><strong>SCIM</strong></li><li><strong>SAML</strong></li></ul><p><br>This value must match how the IdP provides the email attribute used to identify requesters.</p></td></tr><tr><td><strong>Policy Email Attribute</strong></td><td><strong>(Required)</strong> Exact attribute value that contains the user's email address</td></tr><tr><td><strong>IdP</strong></td><td><p><strong>(Required)</strong> Display name of the identity provider Apono uses to match requester</p><p><br>This must exactly match the name as it appears under <strong>IdP Configuration</strong> in the ZPA Admin Portal.</p></td></tr></tbody></table>
7. Click **Next**. The **Secret Store** section expands.
8. [Associate the secret or credentials](/docs/connectors-and-secrets/apono-integration-secret.md).

{% hint style="info" %}
If you select the Apono secret manager, enter the values of the **Client ID** and **Client Secret**.
{% endhint %}

9. Click **Next**. The **Get more with Apono** section expands.
10. Define the **Get more with Apono** settings.

    <table><thead><tr><th width="223">Setting</th><th>Description</th></tr></thead><tbody><tr><td><strong>Credential rotation period (in days)</strong></td><td><p>(Optional) Number of days after which the database credentials must be rotated</p><p>Learn more about the <a href="/docs/architecture-and-security/credentials-rotation-policy.md">Credentials Rotation Policy</a>.</p></td></tr><tr><td><strong>User cleanup after</strong> <strong>access is revoked (in days)</strong></td><td><p>(Optional) Defines the number of days after access has been revoked that the user should be deleted</p><p><br>Learn more about <a href="/docs/architecture-and-security/periodic-user-cleanup-and-deletion.md">Periodic User Cleanup &#x26; Deletion</a>.</p></td></tr><tr><td><strong>Custom Access Details</strong></td><td>(Optional) Instructions explaining how to access this integration's resources<br><br>Upon accessing an integration, a message with these instructions will be displayed to end users in the User Portal. The message may include up to <strong>400 characters</strong>.<br><br>To view the message as it appears to end users, click <strong>Preview</strong>.</td></tr><tr><td><strong>Integration Owner</strong></td><td><p>(Optional) Fallback approver if no <a href="/docs/access-flows/dynamic-access-management/resource-and-integration-owners.md">resource owner</a> is found<br><br>Follow these steps to define one or several integration owners:</p><ol><li>From the <strong>Attribute</strong> dropdown menu, select <strong>User</strong> or <strong>Group</strong> under the relevant identity provider (IdP) platform.</li><li>From the <strong>Value</strong> dropdown menu, select one or multiple users or groups.</li></ol><p><br><strong>NOTE</strong>: When <strong>Resource Owner</strong> is defined, an <strong>Integration Owner</strong> must be defined.</p></td></tr><tr><td><strong>Resource Owner</strong></td><td><p>(Optional) Group or role responsible for managing access approvals or rejections for the resource<br><br>Follow these steps to define one or several <a href="/docs/access-flows/dynamic-access-management/resource-and-integration-owners.md">resource owners</a>:</p><ol><li>Enter a <strong>Key name</strong>. This value is the name of the tag created in your cloud environment.</li><li>From the <strong>Attribute</strong> dropdown menu, select an attribute under the IdP platform to which the key name is associated.<br><br>Apono will use the value associated with the key (tag) to identify the resource owner. When you update the membership of the group or role in your IdP platform, this change is also reflected in Apono.</li></ol><p><br><strong>NOTE</strong>: When this setting is defined, an <strong>Integration Owner</strong> must also be defined.</p></td></tr></tbody></table>
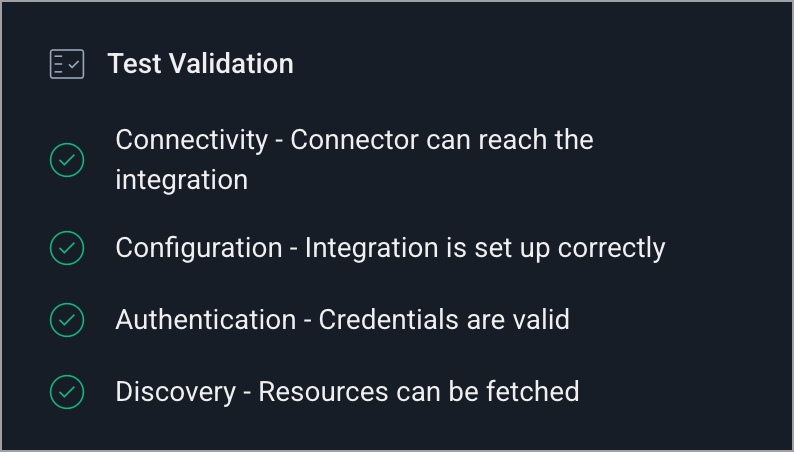
11. (Recommended) Click **Test Integration** to validate the integration.

{% hint style="info" %}
**Test Integration** is available after you have entered or selected values for all required integration fields.

During the test, Apono runs the following validation checks:

* **Connectivity:** The connector can reach the integration.
* **Configuration:** The integration is set up correctly.
* **Authentication:** The credentials are valid.
* **Discovery:** Resources can be fetched.

The **Test Validation** checklist shows the result of each check.

<img src="https://1094436629-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fv6MBfUGvblSdAz31yJXm%2Fuploads%2Fgit-blob-303b3a6834a7c7bf7a1a29aacfb9d323068a9133%2Fintegration-test-validation-new.png?alt=media" alt="" data-size="original">

If a check fails, Apono identifies the failed check and highlights the fields that need correction.
{% endhint %}

12. Click **Confirm**.

<details>

<summary>💡Are you integrating with Apono using Terraform?</summary>

If you want to integrate with Apono using Terraform, follow these steps instead of clicking **Confirm**:

1. At the top of the screen, click **View as Code**. A modal appears with the completed Terraform configuration code.
2. Click to copy the code.
3. Make any additional edits.
4. Deploy the code in your Terraform.

Refer to [Integration Config Metadata](https://docs.apono.io/metadata-for-integration-config/integration-metadata/zscaler-zpa) for more details about the schema definition.

</details>

#### Usage

Use Zscaler ZPA access policy rules as resources in access flows. Apono creates and removes temporary access policy rules to provide time-bound access according to the approval and provisioning rules defined in the flow.

{% hint style="info" %}
Access policy rules created in ZPA appear in Apono after the next discovery cycle completes.
{% endhint %}

Follow the guidance in these articles to define Zscaler ZPA resources in an access flow:

* [Define the resource (Self Serve Access Flows)](https://docs.apono.io/docs/access-flows/creating-access-flows-in-apono/self-serve-access-flows#define-the-resource)
* [Define the resource (Automatic Access Flows)](https://docs.apono.io/docs/access-flows/creating-access-flows-in-apono/automatic-access-flows#define-the-resource)


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.

Perform an HTTP GET request on the current page URL with the `ask` query parameter, and the optional `goal` query parameter:

```
GET https://docs.apono.io/docs/additional-integrations/network-management/zscaler-private-access.md?ask=<question>&goal=<endgoal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is optional and describes the broader end goal you are ultimately trying to accomplish on behalf of the user. GitBook uses it to tailor the answer towards what is most useful for that goal.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.