> For the complete documentation index, see [llms.txt](https://docs.apono.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.apono.io/docs/aws-environment/creating-secrets-for-apono-in-aws-secret-store/access-a-kms-encrypted-secret.md).
# Access a KMS-Encrypted Secret
Enable your Apono connector to read a KMS-encrypted AWS secret
Your Apono connector can read AWS secrets encrypted with Key Management Service (KMS). KMS-encrypted secrets offer several benefits:
* Enhance security with strong encryption
* Easily manage access to secrets using Identity Access Management (IAM) and KMS key policies
* Record who has accessed your secrets, and when, with KMS' built-in auditing
* Meet regulatory and compliance requirements by leveraging KMS encryption for sensitive data
{% hint style="info" %}
For more information on KMS encryption, see [Amazon’s documentation](https://docs.aws.amazon.com/secretsmanager/latest/userguide/security-encryption.html).
{% endhint %}
***
### Prerequisite
Item
Description
AWS secret
Credential information used for authentication and authorization within AWS services
***
### Access a KMS-encrypted secret
Follow these steps to enable your Apono connector to read a KMS-encrypted secret:
1. From the KMS main navigation, click **Customer managed keys**. A table appears with all self-managed keys.
2. Select the key of an Apono-connected secret. The key configuration page appears.
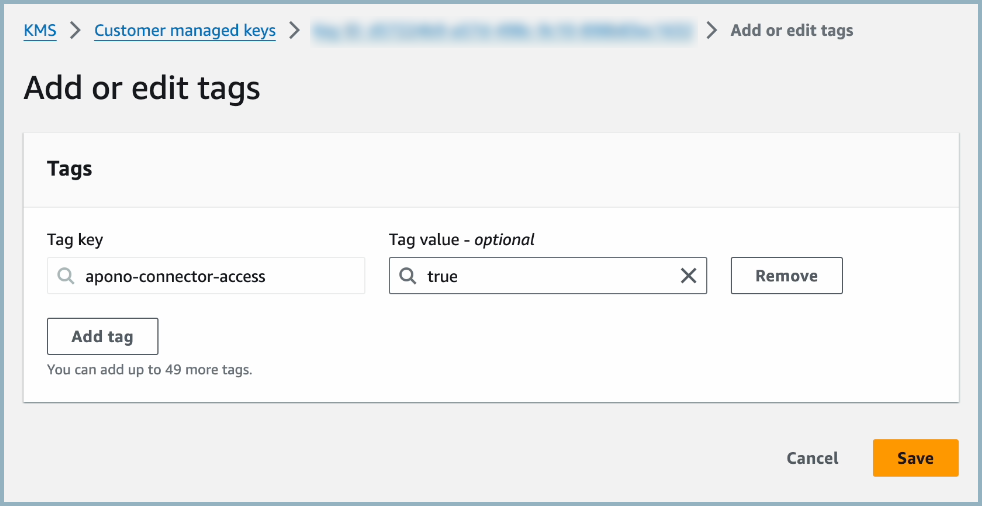
3. Under the **Tags** tab, click **Add tag**. A key-value editor appears.
4. Add the following tag to your KMS encryption key:
Key
Value
apono-connector-access
true
5. Click **Save**.
Your Apono connector can now read your AWS secret with KMS.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.
Perform an HTTP GET request on the current page URL with the `ask` query parameter, and the optional `goal` query parameter:
```
GET https://docs.apono.io/docs/aws-environment/creating-secrets-for-apono-in-aws-secret-store/access-a-kms-encrypted-secret.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is optional and describes the broader end goal you are ultimately trying to accomplish on behalf of the user. GitBook uses it to tailor the answer towards what is most useful for that goal.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.