> For the complete documentation index, see [llms.txt](https://docs.apono.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.apono.io/docs/aws-environment/aws-integrations/aws-rds-mysql.md).

# AWS RDS MySQL

Integrate AWS-managed MySQL databases with Apono for just-in-time access management

MySQL is an open-source relational database management system available through AWS-managed database services.

Through this integration, Apono helps you securely manage access to MySQL databases deployed as either an Amazon RDS for MySQL instance or an Aurora MySQL cluster.

***

### Prerequisites <a href="#prerequisites" id="prerequisites"></a>

<table><thead><tr><th width="212">Item</th><th>Description</th></tr></thead><tbody><tr><td><strong>Apono Connector</strong></td><td>On-prem <a href="https://docs.apono.io/docs/aws-environment/apono-connector-for-aws.md">connection</a> with network access to the RDS for PostgreSQL instance or Aurora PostgreSQL cluster<br><br><strong>Minimum Required Version</strong>: 1.5.3<br><br>Use the following steps to <a href="https://docs.apono.io/docs/aws-environment/apono-connector-for-aws/updating-a-connector-in-aws.md">update an existing connector</a>.</td></tr><tr><td><strong>AWS Command Line (AWS CLI)</strong></td><td><a href="https://docs.aws.amazon.com/cli/latest/userguide/getting-started-install.html">Command-line interface</a> used to manage AWS resources</td></tr><tr><td><strong>MySQL Command Line (MySQL CLI)</strong></td><td><a href="https://dev.mysql.com/doc/refman/8.4/en/mysql.html?utm_source=chatgpt.com">Command-line interface</a> used to connect to and manage MySQL databases</td></tr><tr><td><strong>RDS MySQL Info</strong></td><td><p>Information for the RDS for MySQL instance or Aurora MySQL cluster to be integrated:</p><ul><li><strong>Instance ID</strong>: (RDS) Identifier of the MySQL DB instance</li><li><strong>Cluster ID</strong>: (Aurora) Identifier of the top-level Aurora cluster, above its member instances</li></ul><p>Follow these steps to obtain the instance or cluster ID:</p><ol><li>From the side navigation of the <a href="https://console.aws.amazon.com/rds/">Amazon RDS console</a>, click <strong>Databases</strong>. The <strong>Databases</strong> page appears.</li><li>Under the <strong>DB identifier</strong> column, locate the RDS for MySQL instance or the top-level Aurora MySQL cluster.</li><li>Copy the appropriate instance ID or cluster ID.</li></ol></td></tr><tr><td><strong>AWS Tag</strong></td><td><p>(Optional) Metadata label assigned to AWS resources<br><br>Adding an AWS tag, enables Apono to discover and add resources on your behalf.<br><br>When <a href="https://docs.aws.amazon.com/AmazonRDS/latest/UserGuide/USER_Tagging.html#Tagging.HowTo">adding an AWS tag</a>, use the following information:</p><ul><li><strong>Tag key</strong>: <em>apono-secret</em></li><li><strong>Value</strong>: (<a href="https://docs.apono.io/docs/connectors-and-secrets/apono-integration-secret.md#aws">AWS Secret</a>)</li></ul></td></tr></tbody></table>

***

### Create a MySQL user

You must create a MySQL user for the Apono connector and grant that user permissions to your databases.

Follow these steps to create a user and grant it database permissions:

{% hint style="warning" %}
You can use only **one** authentication method for each MySQL user. An RDS instance or Aurora cluster can support both password and IAM authentication for different users.
{% endhint %}

{% hint style="info" %}
(MySQL 8.0+) Grant the service account the authority to manage other roles. This enables Apono to create, alter, and drop roles. However, this role does not inherently grant specific database access permissions.
{% endhint %}

{% tabs %}
{% tab title="cli" %}

<details>

<summary>Password Authentication</summary>

With password authentication, your database performs all administration of user accounts. You create users with SQL statements such as `CREATE USER`, with the appropriate clause required by the DB engine for specifying passwords.

1. Get your AWS RDS DB details.

```bash
aws rds describe-db-instances \
  --filters "Name=engine,Values=mysql" \
  --query "*[].[Endpoint.Address,Endpoint.Port]"

mysql -h [Endpoint.Address] -P [Endpoint.Port] -u USER_NAME -p
```

2. Connect RDS MySQL.

```bash
mysql -h [Endpoint.Address] -P [Endpoint.Port] -u USER_NAME -p
```

3. Create a username for the Apono connector. The username is arbitrary and can be set according to your preference.
4. Replace `USER_NAME` and `PASSWORD` with your desired credentials.

```sql
CREATE USER 'USER_NAME'@'%' IDENTIFIED BY 'PASSWORD';
```

5. Grant the necessary permissions to the user.

```sql
GRANT SHOW DATABASES ON *.* TO 'USER_NAME'@'%';
GRANT CREATE USER ON *.* TO 'USER_NAME'@'%';  
GRANT UPDATE ON mysql.* TO 'USER_NAME'@'%';
GRANT PROCESS ON *.* TO 'USER_NAME'@'%';
GRANT SELECT ON *.* TO 'USER_NAME'@'%';
GRANT GRANT OPTION ON *.* TO 'USER_NAME'@'%';
GRANT EXECUTE,DROP,SELECT,ALTER,ALTER ROUTINE,CREATE,CREATE ROUTINE,CREATE TEMPORARY TABLES,CREATE VIEW,DELETE,INDEX,INSERT,TRIGGER,UPDATE ON *.* TO 'USER_NAME'@'%';  
GRANT ROLE_ADMIN ON *.* TO 'USER_NAME'@'%';
```

`SHOW DATABASES` Allows the user to view all databases in the RDS instance.\
`CREATE USER` Grants the ability to create new users.\
`UPDATE` Permits updates in the MySQL system database, including user privileges.\
`PROCESS` Allows viewing the server's process list, including all executing queries.\
`ROLE_ADMIN` (MySQL 8.0 and above) Enables the user to create roles, assign permissions to roles, and grant or revoke roles to or from users. This privilege does not inherently grant any specific database access permissions.

</details>

<details>

<summary>IAM Authentication</summary>

You can authenticate to your DB instance using AWS Identity and Access Management (IAM) database authentication. With this authentication method, you don't need to use a password when you connect to a DB instance. Instead, you use an authentication token.

1. Get your AWS RDS DB details.

```bash
aws rds describe-db-instances \
  --filters "Name=engine,Values=mysql" \
  --query "*[].[DBInstanceIdentifier,Endpoint.Address,Endpoint.Port]"
```

2. Enable IAM database authentication.

```bash
aws rds modify-db-instance \
    --db-instance-identifier DBInstanceIdentifier \
    --apply-immediately \
    --enable-iam-database-authentication
```

3. Connect RDS MySQL.

```bash
mysql -h [Endpoint.Address] -P [Endpoint.Port] -u USER_NAME -p
```

4. Create a username for the Apono connector. The username is arbitrary and can be set according to your preference.
5. Replace `USER_NAME` with your desired credentials.

```sql
CREATE USER USER_NAME IDENTIFIED WITH AWSAuthenticationPlugin AS 'RDS';
```

6. Grant the necessary permissions to the user.

```sql
GRANT SHOW DATABASES ON *.* TO 'USER_NAME'@'%';
GRANT CREATE USER ON *.* TO 'USER_NAME'@'%';  
GRANT UPDATE ON mysql.* TO 'USER_NAME'@'%';
GRANT PROCESS ON *.* TO 'USER_NAME'@'%';
GRANT SELECT ON *.* TO 'USER_NAME'@'%';
GRANT EXECUTE,DROP,SELECT,ALTER,ALTER ROUTINE,CREATE,CREATE ROUTINE,CREATE TEMPORARY TABLES,CREATE VIEW,DELETE,INDEX,INSERT,TRIGGER,UPDATE ON *.* TO 'USER_NAME'@'%';  
GRANT GRANT OPTION ON *.* TO 'USER_NAME'@'%';
GRANT ROLE_ADMIN ON *.* TO 'USER_NAME'@'%';
```

`SHOW DATABASES` Allows the user to view all databases in the RDS instance.\
`CREATE USER` Grants the ability to create new users.\
`UPDATE` Permits updates in the MySQL system database, including user privileges.\
`PROCESS` Allows viewing the server's process list, including all executing queries.\
`ROLE_ADMIN` (MySQL 8.0 and above) Enables the user to create roles, assign permissions to roles, and grant or revoke roles to or from users. This privilege does not inherently grant any specific database access permissions.

7. Add this policy to the connector role:

```json
{ "Version": "2012-10-17", "Statement": [ { "Action": "rds-db:connect", "Resource": "arn:aws:rds-db:::dbuser:*/USER_NAME", "Effect": "Allow" } ] }
```

8. To allow a user or role to connect to your DB instance, create the following IAM policy and attach it to your identity center permissions set or role.

```bash
aws iam create-policy --policy-name RDSConnectPolicy --policy-document '{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Effect": "Allow",
            "Action": [
                "rds-db:connect"
            ],
            "Resource": [
                "arn:aws:rds-db:*:*:dbuser:*/${SAML:sub}"
            ]
        },
        {
            "Effect": "Allow",
            "Action": [
                "rds:DescribeDBInstances"
            ],
            "Resource": [
                "arn:aws:rds:*:*:db:*"
            ]
        }
    ]
}'
```

</details>
{% endtab %}

{% tab title="cmd" %}

<details>

<summary>Password Authentication</summary>

With password authentication, your database performs all administration of user accounts. You create users with SQL statements such as `CREATE USER`, with the appropriate clause required by the DB engine for specifying passwords.

1. Get your AWS RDS DB details.

```cmd
aws rds describe-db-instances \
  --filters "Name=engine,Values=mysql" \
  --query "*[].[Endpoint.Address,Endpoint.Port]"

mysql -h [Endpoint.Address] -P [Endpoint.Port] -u USER_NAME -p
```

2. Connect RDS MySQL.

```cmd
mysql -h [Endpoint.Address] -P [Endpoint.Port] -u USER_NAME -p
```

3. Create a username for the Apono connector. The username is arbitrary and can be set according to your preference.
4. Replace `USER_NAME` and `PASSWORD` with your desired credentials.

```sql
CREATE USER 'USER_NAME'@'%' IDENTIFIED BY 'PASSWORD';
```

4. Grant the necessary permissions to the user.

```sql
GRANT SHOW DATABASES ON *.* TO 'USER_NAME'@'%';
GRANT CREATE USER ON *.* TO 'USER_NAME'@'%';  
GRANT UPDATE ON mysql.* TO 'USER_NAME'@'%';
GRANT PROCESS ON *.* TO 'USER_NAME'@'%';
GRANT SELECT ON *.* TO 'USER_NAME'@'%';
GRANT EXECUTE,DROP,SELECT,ALTER,ALTER ROUTINE,CREATE,CREATE ROUTINE,CREATE TEMPORARY TABLES,CREATE VIEW,DELETE,INDEX,INSERT,TRIGGER,UPDATE ON *.* TO 'USER_NAME'@'%';  
GRANT GRANT OPTION ON *.* TO 'USER_NAME'@'%';
GRANT ROLE_ADMIN ON *.* TO 'USER_NAME'@'%';
```

`SHOW DATABASES` Allows the user to view all databases in the RDS instance.\
`CREATE USER` Grants the ability to create new users.\
`UPDATE` Permits updates in the MySQL system database, including user privileges.\
`PROCESS` Allows viewing the server's process list, including all executing queries.\
`ROLE_ADMIN` (MySQL 8.0 and above) Enables the user to create roles, assign permissions to roles, and grant or revoke roles to or from users. This privilege does not inherently grant any specific database access permissions.

</details>

<details>

<summary>IAM Authentication</summary>

You can authenticate to your DB instance using AWS Identity and Access Management (IAM) database authentication. With this authentication method, you don't need to use a password when you connect to a DB instance. Instead, you use an authentication token.

1. Get your AWS RDS DB details.

```cmd
aws rds describe-db-instances \
  --filters "Name=engine,Values=mysql" \
  --query "*[].[DBInstanceIdentifier,Endpoint.Address,Endpoint.Port]"
```

2. Enable IAM database authentication.

```cmd
aws rds modify-db-instance \
    --db-instance-identifier DBInstanceIdentifier \
    --apply-immediately \
    --enable-iam-database-authentication
```

3. Connect RDS MySQL.

```cmd
mysql -h [Endpoint.Address] -P [Endpoint.Port] -u USER_NAME -p
```

4. Create a username for the Apono connector. The username is arbitrary and can be set according to your preference.
5. Replace `USER_NAME` with your desired credentials.

```sql
CREATE USER USER_NAME IDENTIFIED WITH AWSAuthenticationPlugin AS 'RDS';
```

6. Grant the necessary permissions to the user.

```sql
GRANT SHOW DATABASES ON *.* TO 'USER_NAME'@'%';
GRANT CREATE USER ON *.* TO 'USER_NAME'@'%';  
GRANT UPDATE ON mysql.* TO 'USER_NAME'@'%';
GRANT PROCESS ON *.* TO 'USER_NAME'@'%';
GRANT SELECT ON *.* TO 'USER_NAME'@'%';
GRANT EXECUTE,DROP,SELECT,ALTER,ALTER ROUTINE,CREATE,CREATE ROUTINE,CREATE TEMPORARY TABLES,CREATE VIEW,DELETE,INDEX,INSERT,TRIGGER,UPDATE ON *.* TO 'USER_NAME'@'%';  
GRANT GRANT OPTION ON *.* TO 'USER_NAME'@'%';
GRANT ROLE_ADMIN ON *.* TO 'USER_NAME'@'%';
```

`SHOW DATABASES` Allows the user to view all databases in the RDS instance.\
`CREATE USER` Grants the ability to create new users.\
`UPDATE` Permits updates in the MySQL system database, including user privileges.\
`PROCESS` Allows viewing the server's process list, including all executing queries.\
`ROLE_ADMIN` (MySQL 8.0 and above) Enables the user to create roles, assign permissions to roles, and grant or revoke roles to or from users. This privilege does not inherently grant any specific database access permissions.

7. Add this policy to the connector role:

```json
{ "Version": "2012-10-17", "Statement": [ { "Action": "rds-db:connect", "Resource": "arn:aws:rds-db:::dbuser:*/USER_NAME", "Effect": "Allow" } ] }
```

8. To allow a user or role to connect to your DB instance, create the following IAM policy and attach it to your identity center permissions set or role.

```json
aws iam create-policy --policy-name RDSConnectPolicy --policy-document '{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Effect": "Allow",
            "Action": [
                "rds-db:connect"
            ],
            "Resource": [
                "arn:aws:rds-db:*:*:dbuser:*/${SAML:sub}"
            ]
        },
        {
            "Effect": "Allow",
            "Action": [
                "rds:DescribeDBInstances"
            ],
            "Resource": [
                "arn:aws:rds:*:*:db:*"
            ]
        }
    ]
}'
```

</details>
{% endtab %}

{% tab title="console" %}

<details>

<summary>Password Authentication</summary>

With password authentication, your database performs all administration of user accounts. You create users with SQL statements such as `CREATE USER`, with the appropriate clause required by the DB engine for specifying passwords.

1. Sign in to the AWS Management Console and open the Amazon RDS console [Amazon RDS console](https://console.aws.amazon.com/rds/) , and choose your DB instance.
2. Copy the following details:
   * **Endpoint**: The DNS name of the DB instance.
   * **Port**: The port number on which the DB instance accepts connections.
3. Connect to the DB instance using your SQL client using the copied details.
4. Create a user for the Apono connector. Replace `USER_NAME` and `PASSWORD` with your desired credentials.

<pre class="language-sql"><code class="lang-sql"><strong>CREATE USER 'USER_NAME'@'%' IDENTIFIED BY 'PASSWORD';
</strong></code></pre>

5. Grant the necessary permissions to the user.

```sql
GRANT SHOW DATABASES ON *.* TO 'USER_NAME'@'%';
GRANT CREATE USER ON *.* TO 'USER_NAME'@'%';  
GRANT UPDATE ON mysql.* TO 'USER_NAME'@'%';
GRANT PROCESS ON *.* TO 'USER_NAME'@'%';
GRANT SELECT ON *.* TO 'USER_NAME'@'%';
GRANT EXECUTE,DROP,SELECT,ALTER,ALTER ROUTINE,CREATE,CREATE ROUTINE,CREATE TEMPORARY TABLES,CREATE VIEW,DELETE,INDEX,INSERT,TRIGGER,UPDATE ON *.* TO 'USER_NAME'@'%';  
GRANT GRANT OPTION ON *.* TO 'USER_NAME'@'%';
GRANT ROLE_ADMIN ON *.* TO 'USER_NAME'@'%';
```

`SHOW DATABASES` Allows the user to view all databases in the RDS instance.\
`CREATE USER` Grants the ability to create new users.\
`UPDATE` Permits updates in the MySQL system database, including user privileges.\
`PROCESS` Allows viewing the server's process list, including all executing queries.\
`ROLE_ADMIN` (MySQL 8.0 and above) Enables the user to create roles, assign permissions to roles, and grant or revoke roles to or from users. This privilege does not inherently grant any specific database access permissions.

</details>

<details>

<summary>IAM Authentication</summary>

You can authenticate to your DB instance using AWS Identity and Access Management (IAM) database authentication. With this authentication method, you don't need to use a password when you connect to a DB instance. Instead, you use an authentication token.

1. Enable IAM database authentication
   1. Open the [Amazon RDS console](https://console.aws.amazon.com/rds/).
   2. In the navigation pane, choose Databases.
   3. Choose the DB instance that you want to modify.
   4. Make sure that the DB instance is compatible with IAM authentication. Check the compatibility requirements in Region and version availability.
   5. Choose Modify.
   6. In the Database authentication section, choose Password and IAM database authentication to enable IAM database authentication.
   7. Choose Password authentication or Password and Kerberos authentication to disable IAM authentication.
   8. Choose Continue.
   9. To apply the changes immediately, choose Immediately in the Scheduling of modifications section.
   10. Choose Modify DB instance.
2. Copy the following RDS SQL details:

* **Endpoint**: The DNS name of the DB instance.
* **Port**: The port number on which the DB instance accepts connections.

3. Connect to the DB instance using your SQL client using the copied details.
4. Create a username for the Apono connector. The username is arbitrary and can be set according to your preference.
5. Replace `USER_NAME` with your desired credentials.

```sql
CREATE USER USER_NAME IDENTIFIED WITH AWSAuthenticationPlugin AS 'RDS';
```

5. Grant the necessary permissions to the user.

```sql
GRANT SHOW DATABASES ON *.* TO 'USER_NAME'@'%';
GRANT CREATE USER ON *.* TO 'USER_NAME'@'%';  
GRANT UPDATE ON mysql.* TO 'USER_NAME'@'%';
GRANT PROCESS ON *.* TO 'USER_NAME'@'%';
GRANT SELECT ON *.* TO 'USER_NAME'@'%';
GRANT EXECUTE,DROP,SELECT,ALTER,ALTER ROUTINE,CREATE,CREATE ROUTINE,CREATE TEMPORARY TABLES,CREATE VIEW,DELETE,INDEX,INSERT,TRIGGER,UPDATE ON *.* TO 'USER_NAME'@'%';  
GRANT GRANT OPTION ON *.* TO 'USER_NAME'@'%';
GRANT ROLE_ADMIN ON *.* TO 'USER_NAME'@'%';
```

`SHOW DATABASES` Allows the user to view all databases in the RDS instance.\
`CREATE USER` Grants the ability to create new users.\
`UPDATE` Permits updates in the MySQL system database, including user privileges.\
`PROCESS` Allows viewing the server's process list, including all executing queries.\
`ROLE_ADMIN` (MySQL 8.0 and above) Enables the user to create roles, assign permissions to roles, and grant or revoke roles to or from users. This privilege does not inherently grant any specific database access permissions.

6. Add this policy to the connector role:

```json
{ "Version": "2012-10-17", "Statement": [ { "Action": "rds-db:connect", "Resource": "arn:aws:rds-db:::dbuser:*/USER_NAME", "Effect": "Allow" } ] }
```

7. To allow a user or role to connect to your DB instance, create the following IAM policy and attach it to your identity center permissions set or role.

```json
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Effect": "Allow",
        "Action": [
          "rds-db:connect"
        ],
      "Resource": [
        "arn:aws:rds-db:*:*:dbuser:*/${SAML:sub}"
      ]
    },
    {
      "Effect": "Allow",
        "Action": [
          "rds:DescribeDBInstances"
        ],
        "Resource": [
          "arn:aws:rds:*:*:db:*"
        ]
      }
  ]
}
```

</details>
{% endtab %}
{% endtabs %}

***

### Integrate AWS RDS for MySQL

{% hint style="success" %}
You can also use the steps below to integrate with Apono using Terraform.

In step **12**, instead of clicking **Confirm**, follow the **Are you integrating with Apono using Terraform?** guidance.
{% endhint %}

Follow these steps to complete the integration:

1. On the [**Catalog**](https://app.apono.io/catalog?search=aws+rds+mysql) tab, click **AWS RDS MySQL**. The **Connect Integration** page appears.
2. Under **Discovery**, click one or more resource types to sync with Apono.

{% hint style="info" %}
Apono automatically discovers and syncs the selected resource types in the environment. After syncing, you can manage **Access Flows** to these resources.
{% endhint %}

3. Click **Next**. The **Apono connector** section expands.
4. From the dropdown menu, select a connector. Choosing a connector links Apono to all the services available on the account where the connector is located.

{% hint style="success" icon="lightbulb" %}
If the desired connector is not listed, click **+ Add new connector** and follow the instructions for creating an [AWS connector](https://docs.apono.io/docs/aws-environment/apono-connector-for-aws.md).
{% endhint %}

5. Click **Next**. The **Integration Config** section expands.
6. Define the **Integration Config** settings.

   <table><thead><tr><th width="210">Setting</th><th>Description</th></tr></thead><tbody><tr><td><strong>Integration Name</strong></td><td>Unique, alphanumeric, user-friendly name used to identify this integration when constructing an access flow</td></tr><tr><td><strong>Auth Type</strong></td><td><p>Authentication method for the MySQL service account user:</p><ul><li><strong>IAM Auth</strong>: IAM authentication</li><li><strong>User / Password</strong>: Built-in authentication</li></ul></td></tr><tr><td><strong>Region</strong></td><td>Location where the MySQL database is deployed</td></tr><tr><td><strong>Instance ID</strong></td><td>(RDS) Unique identifier of the MySQL instance<br><br><strong>Leave empty when integrating an Aurora cluster.</strong></td></tr><tr><td><strong>Cluster ID</strong></td><td><p>(Aurora) Unique identifier of the Aurora MySQL DB cluster</p><p><strong>Leave empty when integrating a regular RDS instance.</strong></p></td></tr></tbody></table>
7. Click **Next**. The **Secret Store** section expands.
8. [Associate the secret or credentials.](https://docs.apono.io/docs/connectors-and-secrets/apono-integration-secret.md)

{% hint style="info" %}
A secret is **not** needed for IAM authentication.

If you select the **Apono** secret manager, enter the value of the **Username** and **Password** for the RDS MySQL Apono user.
{% endhint %}

9. Click **Next**. The **Get more with Apono** section expands.
10. Define the **Get more with Apono** settings.

    <table><thead><tr><th width="193">Setting</th><th>Description</th></tr></thead><tbody><tr><td><strong>Credential Rotation</strong></td><td>(Optional) Number of days after which the database credentials must be rotated<br><br>Learn more about the <a href="https://docs.apono.io/docs/architecture-and-security/credentials-rotation-policy.md">Credentials Rotation Policy</a>.</td></tr><tr><td><strong>User cleanup after access is revoked (in days)</strong></td><td><p>(Optional) Defines the number of days after access has been revoked that the user should be deleted</p><p><br>Learn more about <a href="https://docs.apono.io/docs/architecture-and-security/periodic-user-cleanup-and-deletion.md">Periodic User Cleanup &#x26; Deletion</a>.</p></td></tr><tr><td><strong>Custom Access Details</strong></td><td>(Optional) Instructions explaining how to access this integration's resources<br><br>Upon accessing an integration, a message with these instructions will be displayed to end users in the User Portal. The message may include up to <strong>400 characters</strong>.<br><br>To view the message as it appears to end users, click <strong>Preview</strong>.</td></tr><tr><td><strong>Integration Owner</strong></td><td><p>(Optional) Fallback approver if no <a href="https://docs.apono.io/docs/access-flows/dynamic-access-management/resource-and-integration-owners.md">resource owner</a> is found<br><br>Follow these steps to define one or several integration owners:</p><ol><li>From the <strong>Attribute</strong> dropdown menu, select <strong>User</strong> or <strong>Group</strong> under the relevant identity provider (IdP) platform.</li><li>From the <strong>Value</strong> dropdown menu, select one or multiple users or groups.</li></ol><p><br><strong>NOTE</strong>: When <strong>Resource Owner</strong> is defined, an <strong>Integration Owner</strong> must be defined.</p></td></tr><tr><td><strong>Resource Owner</strong></td><td><p>(Optional) Group or role responsible for managing access approvals or rejections for the resource<br><br>Follow these steps to define one or several <a href="https://docs.apono.io/docs/access-flows/dynamic-access-management/resource-and-integration-owners.md">resource owners</a>:</p><ol><li>Enter a <strong>Key name</strong>. This value is the name of the tag created in your cloud environment.</li><li>From the <strong>Attribute</strong> dropdown menu, select an attribute under the IdP platform to which the key name is associated.<br><br>Apono will use the value associated with the key (tag) to identify the resource owner. When you update the membership of the group or role in your IdP platform, this change is also reflected in Apono.</li></ol><p><br><strong>NOTE</strong>: When this setting is defined, an <strong>Integration Owner</strong> must also be defined.</p></td></tr></tbody></table>
11. (Recommended) Click **Test Integration** to validate the integration.

{% hint style="info" %}
**Test Integration** is available after you have entered or selected values for all required integration fields.

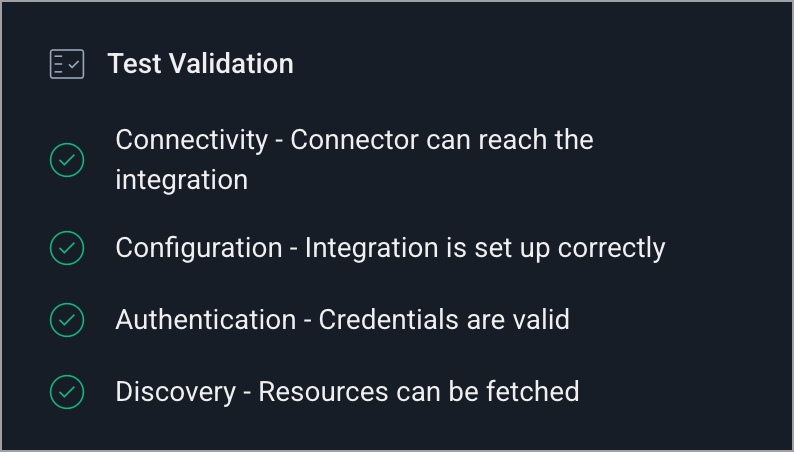
During the test, Apono runs the following validation checks:

* **Connectivity:** The connector can reach the integration.
* **Configuration:** The integration is set up correctly.
* **Authentication:** The credentials are valid.
* **Discovery:** Resources can be fetched.

The **Test Validation** checklist shows the result of each check.

<img src="https://1094436629-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fv6MBfUGvblSdAz31yJXm%2Fuploads%2Fgit-blob-303b3a6834a7c7bf7a1a29aacfb9d323068a9133%2Fintegration-test-validation-new.png?alt=media" alt="" data-size="original">

If a check fails, Apono identifies the failed check and highlights the fields that need correction.<br>
{% endhint %}

12. Click **Confirm**.

<details>

<summary>💡Are you integrating with Apono using Terraform?</summary>

If you want to integrate with Apono using Terraform, follow these steps instead of clicking **Confirm**:

1. At the top of the screen, click **View as Code**. A modal appears with the completed Terraform configuration code.
2. Click to copy the code.
3. Make any additional edits.
4. Deploy the code in your Terraform.

Refer to [Integration Config Metadata](https://docs.apono.io/metadata-for-integration-config/integration-metadata/aws-rds-mysql) for more details about the schema definition.

</details>

#### Usage

Now that the integration is complete, you can add AWS RDS MySQL clusters and databases as resources in an access flow. This allows requesters to securely request temporary access to those resources based on your approval and provisioning rules.

Follow the guidance in these articles to define AWS RDS MySQL resources:

* [Define the resource (Self Serve Access Flows)](https://docs.apono.io/docs/access-flows/creating-access-flows-in-apono/self-serve-access-flows.md#define-the-resource)
* [Define the resource (Automatic Access Flows)](https://docs.apono.io/docs/access-flows/creating-access-flows-in-apono/automatic-access-flows.md#define-the-resource)


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://docs.apono.io/docs/aws-environment/aws-integrations/aws-rds-mysql.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.