> For the complete documentation index, see [llms.txt](https://docs.apono.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.apono.io/docs/additional-integrations/network-management/aws-ec2-ssh-servers.md).

# AWS EC2 SSH Servers

How to integrate with your EC2 SSH Servers with Apono for JIT access

Amazon Elastic Compute Cloud (EC2) is a cloud computing service that provides scalable virtual servers for running applications and workloads. Teams often connect to EC2 instances over SSH to debug, develop, and troubleshoot, but standing SSH access increases the risk of credential sprawl and unauthorized access to critical infrastructure.

You can integrate Amazon EC2 SSH servers with Apono to give your team just-in-time access through access flows. Admins can define which servers users, groups, and shifts can request, along with approval requirements and access durations. When a request is approved, Apono issues a certificate that grants access to the server and adds the requester to the Linux groups that match the requested access. Apono may also use the user's default Linux group.

### Prerequisites

<table><thead><tr><th width="211">Item</th><th>Description</th></tr></thead><tbody><tr><td><strong>Apono Connector</strong></td><td><p>On-prem connection serving as a bridge between an SSH server and Apono:</p><ul><li><a href="/docs/aws-environment/apono-connector-for-aws.md">AWS</a></li><li><a href="/docs/azure-environment/apono-connector-for-azure.md">Azure</a></li><li><a href="/docs/gcp-environment/apono-connector-for-gcp.md">GCP</a></li><li><a href="/docs/kubernetes-environment/apono-connector-for-kubernetes.md">Kubernetes</a></li></ul><p><strong>Minimum Required Version</strong>: 1.4.0</p><p>Learn how to update an existing <a href="/docs/aws-environment/apono-connector-for-aws/updating-a-connector-in-aws.md">AWS</a>, <a href="/docs/azure-environment/apono-connector-for-azure/updating-a-connector-in-azure.md">Azure</a>, <a href="/docs/gcp-environment/apono-connector-for-gcp/updating-a-connector-in-google-cloud.md">GCP</a>, or <a href="/docs/kubernetes-environment/apono-connector-for-kubernetes/updating-a-kubernetes-connector.md">Kubernetes</a> connector.</p></td></tr><tr><td><strong>User with Key Pair Authentication</strong></td><td><p>Dedicated SSH server user account that authenticates with SSH key pairs</p><p>In the sudoers file, add the following line to allow Apono to execute commands with sudo privileges without a password prompt.</p><pre class="language-sh"><code class="lang-sh">apono ALL=(ALL) NOPASSWD:ALL
</code></pre></td></tr><tr><td><strong>Apono Secret</strong></td><td><p>Value generated with the credentials of the SSH server user</p><p><a href="/docs/connectors-and-secrets/apono-integration-secret.md">Create your secret</a> based on your SSH server private key in base64 format.</p><pre><code>"key": "base64_private_key"
"value": "&#x3C;SSH_SERVER_PRIVATE_KEY>"
</code></pre><p>To find the private key in base64 format, run the following command.</p><pre class="language-sh"><code class="lang-sh">cat /PATH-TO-KEY/key.pem | base64
</code></pre><p><em>Apono does not store credentials. The Apono connector uses the secret to communicate with services in your environment and separates the Apono web app from the environment for</em> <a href="/docs/about-apono/security-and-architecture.md"><em>maximal</em></a> <em>security.</em></p></td></tr><tr><td><strong>User Groups</strong></td><td><p>(Optional) User groups representing access to the SSH servers</p><p><strong>Default</strong>: Default</p><p>The default represents access to the server with the user's default Linux group.</p></td></tr></tbody></table>

### Integrate AWS EC2 SSH servers

<figure><img src="https://1094436629-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fv6MBfUGvblSdAz31yJXm%2Fuploads%2Fgit-blob-fe904e38db29c140dc634f5ba824c61d74cfe2e0%2Fimage%20(36).png?alt=media" alt=""><figcaption></figcaption></figure>

{% hint style="success" %}
You can also use the steps below to integrate with Apono using Terraform.

In step **11**, instead of clicking **Confirm**, follow the **Are you integrating with Apono using Terraform?** guidance.
{% endhint %}

Follow these steps to complete the integration:

1. On the [**Catalog**](https://app.apono.io/catalog?search=ssh) tab, click **AWS EC2** **SSH**. The **Connect Integration** page appears.
2. Under **Discovery**, click **Next**. The **Apono connector** section expands.
3. From the dropdown menu, select a connector. Choosing a connector links Apono to all the services available on the account where the connector is located.

{% hint style="info" %}
If the desired connector is not listed, click **+ Add new connector** and follow the instructions for creating a connector ([AWS](/docs/aws-environment/apono-connector-for-aws.md), [Azure](/docs/azure-environment/apono-connector-for-azure.md), [GCP](/docs/gcp-environment/apono-connector-for-gcp.md), [Kubernetes](/docs/kubernetes-environment/apono-connector-for-kubernetes.md)).
{% endhint %}

4. Click **Next**. The **Integration Config** page appears.
5. Define the **Integration Config** settings.

<table><thead><tr><th width="211">Setting</th><th>Description</th></tr></thead><tbody><tr><td><strong>Integration Name</strong></td><td>Unique, alphanumeric, user-friendly name used to identify this integration when constructing an access flow</td></tr><tr><td><strong>Region</strong></td><td>AWS region where your EC2 SSH servers are located</td></tr><tr><td><strong>User</strong></td><td>User Apono uses to authenticate to your SSH servers</td></tr><tr><td><strong>User Groups</strong></td><td>(Optional) Names of groups in the server representing the sudoer role</td></tr><tr><td><strong>User's Login Shell</strong></td><td>(Optional) Command-line interface program used to log in to an account via SSH</td></tr><tr><td><strong>User Key Name</strong></td><td>(Optional) Filename of the SSH key pair used for authentication</td></tr><tr><td><strong>IP Type Preference</strong></td><td><p>(Optional) IP address type Apono uses to connect to your servers:</p><ul><li>(Default) <strong>Public</strong></li><li><strong>Private</strong></li></ul></td></tr><tr><td><strong>Cross Account Role ARN</strong></td><td><p>(Optional) ARN of the role Apono assumes when accessing EC2</p><p>servers in another AWS account<br></p><p>Use the format <code>arn:aws:iam::[ACCOUNT_ID]:role/[ROLE_NAME]</code>.</p></td></tr></tbody></table>

6. Click **Next**. The **Secret Store** section expands.
7. [Associate the secret or credentials](/docs/connectors-and-secrets/apono-integration-secret.md).

{% hint style="info" %}
If you select the **Apono** secret manager, enter your AWS EC2 SSH **Base64 Private Key** and **Password**.
{% endhint %}

8. Click **Next**. The **Get more with Apono** section expands.
9. Define the **Get more with Apono** settings.

<table><thead><tr><th width="212">Setting</th><th>Description</th></tr></thead><tbody><tr><td><strong>Credential Rotation</strong></td><td><p>(Optional) Number of days after which the database credentials must be rotated</p><p>Learn more about the <a href="/docs/architecture-and-security/credentials-rotation-policy.md">Credentials Rotation Policy</a>.</p></td></tr><tr><td><strong>User cleanup after access is revoked (in days)</strong></td><td><p>(Optional) Defines the number of days after access has been revoked that the user should be deleted</p><p>Learn more about <a href="/docs/architecture-and-security/periodic-user-cleanup-and-deletion.md">Periodic User Cleanup &#x26; Deletion</a>.</p></td></tr><tr><td><strong>Custom Access Details</strong></td><td>(Optional) Instructions explaining how to access this integration's resources<br><br>Upon accessing an integration, a message with these instructions will be displayed to end users in the User Portal. The message may include up to <strong>400 characters</strong>.<br><br>To view the message as it appears to end users, click <strong>Preview</strong>.</td></tr><tr><td><strong>Integration Owner</strong></td><td><p>(Optional) Fallback approver if no <a href="/docs/access-flows/dynamic-access-management/resource-and-integration-owners.md">resource owner</a> is found<br><br>Follow these steps to define one or several integration owners:</p><ol><li>From the <strong>Attribute</strong> dropdown menu, select <strong>User</strong> or <strong>Group</strong> under the relevant identity provider (IdP) platform.</li><li>From the <strong>Value</strong> dropdown menu, select one or multiple users or groups.</li></ol><p><strong>NOTE</strong>: When <strong>Resource Owner</strong> is defined, an <strong>Integration Owner</strong> must be defined.</p></td></tr><tr><td><strong>Resource Owner</strong></td><td><p>(Optional) Group or role responsible for managing access approvals or rejections for the resource<br><br>Follow these steps to define one or several <a href="/docs/access-flows/dynamic-access-management/resource-and-integration-owners.md">resource owners</a>:</p><ol><li>Enter a <strong>Key name</strong>. This value is the name of the tag created in your cloud environment.</li><li>From the <strong>Attribute</strong> dropdown menu, select an attribute under the IdP platform to which the key name is associated.<br><br>Apono will use the value associated with the key (tag) to identify the resource owner. When you update the membership of the group or role in your IdP platform, this change is also reflected in Apono.</li></ol><p><strong>NOTE</strong>: When this setting is defined, an <strong>Integration Owner</strong> must also be defined.</p></td></tr></tbody></table>

10. (Recommended) Click **Test Integration** to validate the integration.

{% hint style="info" %}
**Test Integration** is available after you have entered or selected values for all required integration fields.

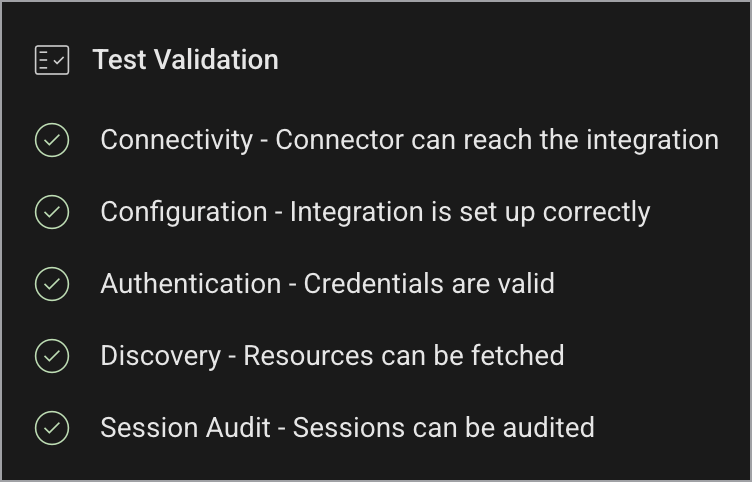
During the test, Apono runs the following validation checks:

* **Connectivity:** The connector can reach the integration.
* **Configuration:** The integration is set up correctly.
* **Authentication:** The credentials are valid.
* **Discovery:** Resources can be fetched.
* **Session Audit**: (Beta) Sessions can be audited. This check appears only when session audit is enabled for the integration. It verifies that the connector:
  * Has session audit enabled in its configuration.
  * Has a proxy host and destination S3 bucket configured.
  * Can validate the S3 bucket setup.

The **Test Validation** checklist shows the result of each check.

<img src="https://1094436629-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fv6MBfUGvblSdAz31yJXm%2Fuploads%2Fgit-blob-791ccff629e6f9fac78fdc1d4da6c12e66787a72%2Fsession-audit-test-integration.png?alt=media" alt="" data-size="original">

If a check fails, Apono identifies the failed check and highlights the fields that need correction.
{% endhint %}

11. Click **Confirm**.

<details>

<summary>💡Are you integrating with Apono using Terraform?</summary>

If you want to integrate with Apono using Terraform, follow these steps instead of clicking **Confirm**:

1. At the top of the screen, click **View as Code**. A modal appears with the completed Terraform configuration code.
2. Click to copy the code.
3. Make any additional edits.
4. Deploy the code in your Terraform.

Refer to [Integration Config Metadata](https://docs.apono.io/metadata-for-integration-config/integration-metadata/aws-ec2-ssh) for more details about the schema definition.

</details>

### Usage

Now that the integration is complete, you can add AWS EC2 SSH to define the resource in an access flow. This allows requesters to securely access secrets stored in your Apono service, based on the access flow’s approval and provisioning rules.

Follow the guidance in these articles to define the resource using AWS EC2 SSH:

* [Define the resource (Self Serve Access Flows)](https://docs.apono.io/docs/access-flows/creating-access-flows-in-apono/self-serve-access-flows#define-the-resource)
* [Define the resource (Automatic Access Flows)](https://docs.apono.io/docs/access-flows/creating-access-flows-in-apono/automatic-access-flows#define-the-resource)


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://docs.apono.io/docs/additional-integrations/network-management/aws-ec2-ssh-servers.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.